10大最常见的加密货币骗局及其识别方法
下面列出的十种反复出现的模式让普通人蒙受了真金白银的损失。排序以实用性为准,而不是严格的排行榜,因为官方投诉数据、链上追踪和私人研究衡量的各是不同的东西。每个条目都会告诉你这种骗局从受害者视角看是什么样子、暴露它的破绽,以及一个可以当场使用的一句话测试。犯罪分子会把这些模式串联起来使用,而中过一次招的人正是下一场骗局最青睐的目标。
搜索完整的库或关注从基本原理到高级操作安全性的主题。
60 文章
需要定义吗?打开术语表下面列出的十种反复出现的模式让普通人蒙受了真金白银的损失。排序以实用性为准,而不是严格的排行榜,因为官方投诉数据、链上追踪和私人研究衡量的各是不同的东西。每个条目都会告诉你这种骗局从受害者视角看是什么样子、暴露它的破绽,以及一个可以当场使用的一句话测试。犯罪分子会把这些模式串联起来使用,而中过一次招的人正是下一场骗局最青睐的目标。
Address poisoning is a payment-redirection attack that plants attacker-controlled lookalike addresses in a victim's transaction history, using zero-value token events, counterfeit tokens or tiny transfers, so that a later copy from that history selects the attacker's address.
AI voice-clone and deepfake crypto scams are a form of impersonation fraud that uses generative models to copy the voice, face or writing of someone the target trusts, such as a relative, executive, support agent or celebrity, to press for an urgent crypto transfer or login codes.
有些市场事件因规模而重要。这一事件因其内部结构而重要。市场结构分析师多年来记录在案的每一个结构性弱点,创纪录杠杆、循环收益策略、全仓抵押、内部定价预言机、自动减仓、缺失的熔断机制、割裂的价格发现以及不透明的清算报告,在同一个小时内依次引爆,全程公开,留下了一条将被研究十年的数据轨迹。这篇旗舰分析重建了那个小时,量化了可以量化的内容,然后做了大多数报道没有做的事:把四种相互竞争的解释连同其证据、支持者和弱点并列呈现,因为在最重要的问题上,现有记录仍处于公开争议之中。
A custodial crypto exchange is a company that matches trades and holds customers' crypto-assets in wallets it controls, recording balances in its own ledger. Whether a balance is the customer's property or a debt the company owes depends on the account agreement and the law governing the contracting entity, and it is usually tested only if the company fails.
如何使用本术语表
本指南同时面向两类读者。如果你刚接触加密货币,通俗的讲解和危险信号清单能给你一条实用的安全底线。如果你已有经验,关于授权机制、盗取程序基础设施、洗钱模式和运营安全的章节会深入得多。这里没有任何内容要求你购买什么。目标是:读完这篇文章,你比大多数加密货币用户更难被骗。
Crypto wallet security is a set of operational practices that keeps control of a self-custodied wallet's keys with its owner during everyday use. It covers five surfaces: the device that signs, the signatures granted to applications, the backups that restore access, the transfers sent, and the vendor software and firmware the wallet runs.
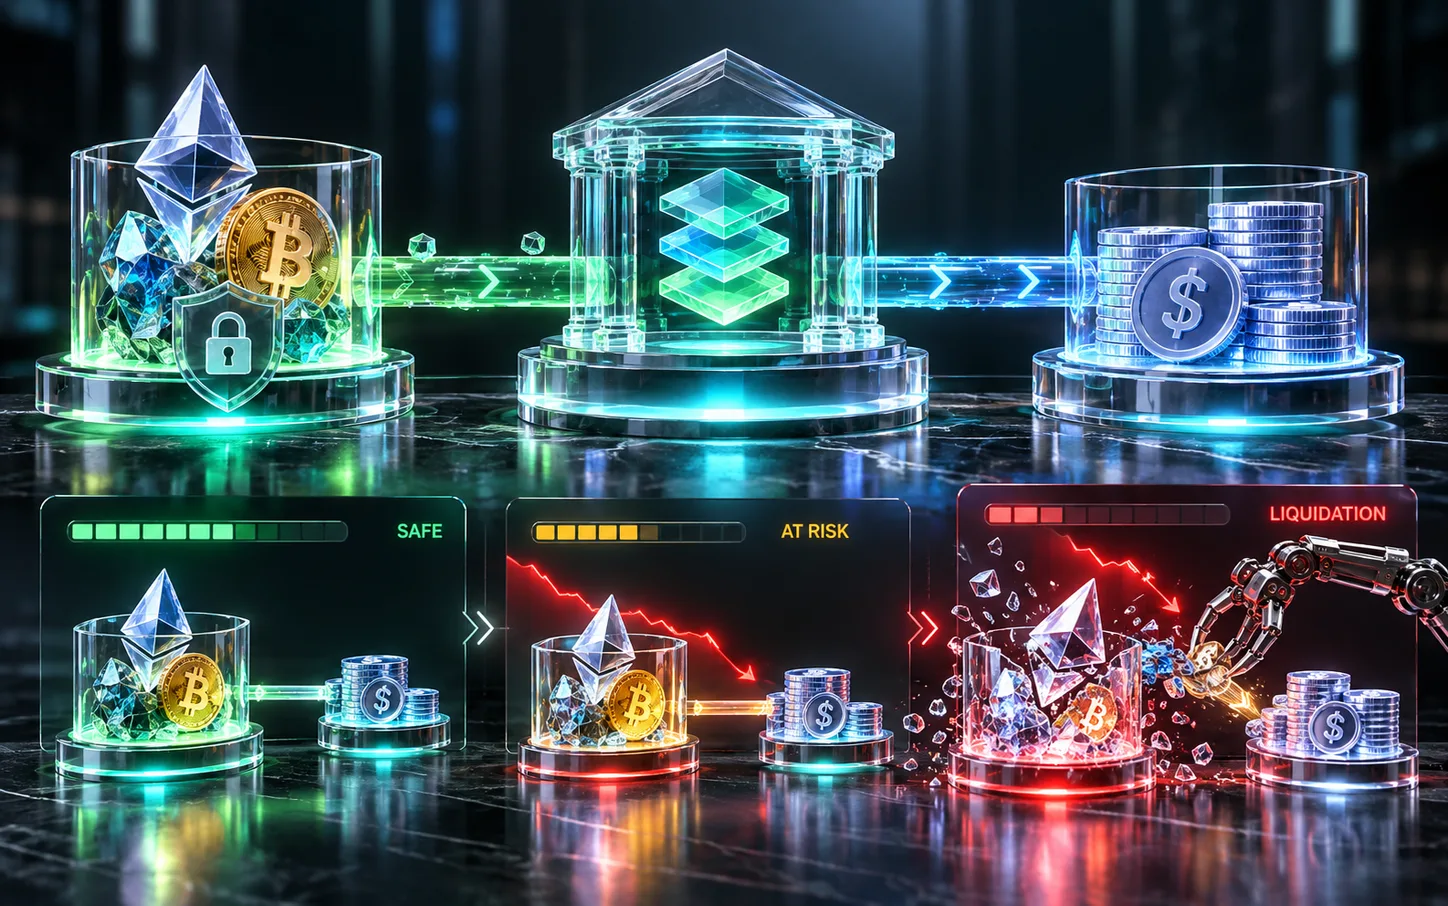
Overcollateralised DeFi lending, as run by Aave, Compound and Sky, is a form of crypto credit that runs on smart contracts and secures each loan with collateral worth more than the debt. The protocol scales the collateral's value by a liquidation threshold and compares it with the debt.
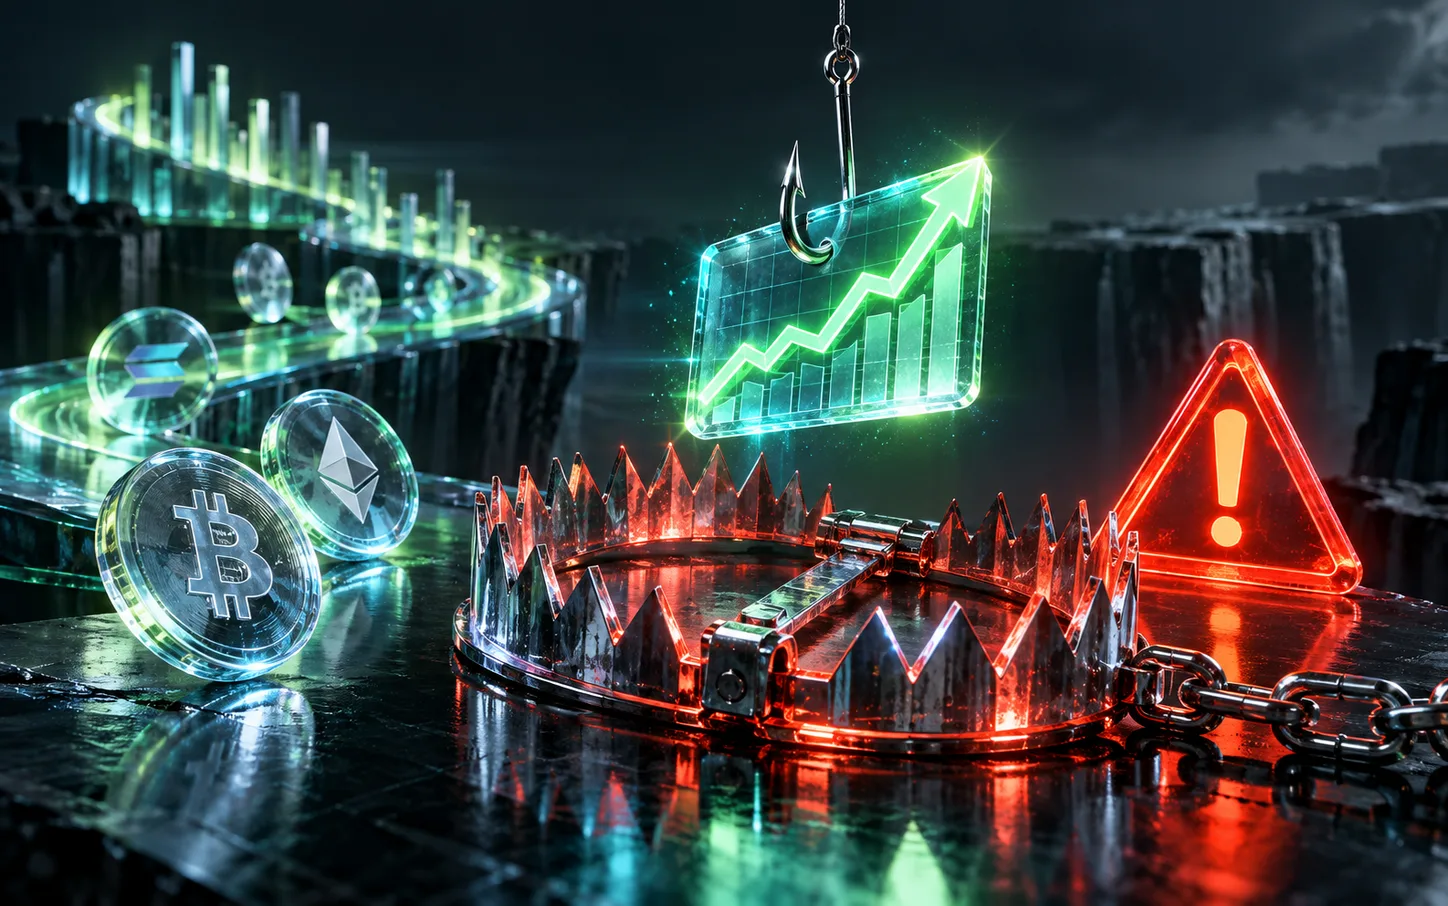
A guaranteed-return offer is an investment pitch promising a fixed, above-market return with little or no claimed risk. The SEC lists "high returns with little or no risk" first among its Ponzi scheme warning signs.
图1. 一笔交易会经历几种不同的状态。“钱包已看到”“在某个内存池中”“已打包”“safe”和“已结算”并不是可以互换的说法。
加密货币通过将加密授权与复制账本相结合来运作。钱包构建精确的交易,并由私钥、智能账户策略或签名定额对其进行授权。独立节点验证交易,区块生产者对有效交易进行排序,共识规则选出规范历史。被纳入区块即为首次确认;额外的工作量证明、验证者投票或检查点可降低重组织风险,直至收款方将付款视为已结算。
钱包恢复是一套在丢失后恢复签名权限的机制:设备故障、助记词损毁、所有者遗忘或所有者去世。基于助记词的恢复可从一条助记词中再生所有密钥;基于社交关系和监护人的恢复通过指定方的法定人数重新组建权限;MPC恢复则无需任何完整的密钥即可刷新或重建分布式份额。 继承是恢复机制中最棘手的情况:当唯一了解设置的人离世后,如何依法将访问权限转移给他人。
监管是有效的初步筛选标准,但并非安全保证。请核实合同中明确列出的公司名称(而非仅品牌名称),并了解哪些保护措施适用、哪些不适用。 在欧盟,MiCA过渡期已于2026年7月1日结束。由于该日期之后规则和授权状态可能会发生变化,请在阅读本文时确认当前状况:查阅欧洲证券和市场管理局(ESMA)注册信息,并确认签约主体(而非仅其关联公司)已获得授权。 如果服务商支持,请使用通行密钥或硬件安全密钥。如果不支持,请使用密码管理器生成的唯一密码配合身份验证应用。短信验证码是一种安全性较低的备选方案,特别是对于被针对的用户而言。 身份核查要求因地而异。受监管的虚拟资产服务提供商通常需履行客户尽职调查义务,但所需文件、时限及门槛因服务类型和司法管辖区而异。
确保加密资产安全,首先且最关键的是一个管理问题。实际上,谁能生成正确的签名,谁就控制着资金,因此从钓鱼短信到住宅火灾,每一种威胁归根结底都关乎签名权限的归属以及哪些因素可能对其造成影响。 威胁来自两个方向,而大多数人只防范其中之一。2025年,黑客攻击造成的盗窃损失约为34亿美元,而欺诈性诈骗造成的损失则是其数倍。 资产损失则更为隐蔽且难以量化:River公司2025年的托管分析估计,约有157万枚比特币可能已永久丢失,但同时提醒,真实数字以及其中有多少是真正丢失而非仅仅处于休眠状态,目前尚无法确定。 单点故障始终是挥之不去的隐患。一个密码、一个电话号码、一句助记词、一个人:只要你的配置中存在任何“唯一”的环节,那里就将成为系统崩溃的突破口。现代托管方案(包括多签名和多方计算等选项)正是为了消除这些单点故障而存在的,如今这些技术已普及到普通消费者的…
最初一小时内速度至关重要,且需先诊断后行动:交易所账户被接管、您签署了恶意授权,以及密钥或助记词泄露,这三种紧急情况各有不同的解决方案。采取错误的解决方案将白白浪费这一小时。 通用的第一步是利用未受感染的设备止损:按资产价值高低顺序,将剩余资产转移至安全处、冻结可冻结的资产,并撤销可撤销的授权。一旦钱包或账户遭到入侵,就永远不要再信任它;目标是撤离资产,绝非修复。 即使恢复看起来毫无希望,也要进行报案:向平台报案,其冻结措施可以抢在洗钱者之前;向执法部门报案,在美国是FBI的IC3,在英国大部分地区是“Report Fraud”,这些案件档案将推动实际发生的逮捕和扣押行动。要设定合理的预期:大多数被盗的链上资金永远无法追回。 事后处理中存在两个陷阱和一份馈赠。陷阱一是“恢复诈骗者”——他们会将公开受骗的受害者作为二次攻击的目标;陷阱二是“羞耻感”—…
签名钓鱼型资金抽取攻击通过获取受害者自愿签署的授权来实施盗取;泄露密钥型清扫攻击则利用被盗密钥生成的授权。这两种情况均未涉及密码学漏洞。攻击者通过链上批准、链下许可签名,以及自2025年起实施的EIP-7702委托机制,滥用了授权模型。 ScamSniffer追踪的EVM资金抽取攻击损失从2024年的约4.
Stablecoin regulation is a body of law that governs who may issue a token pegged to an official currency, what assets must back it, who may redeem it and on what terms, what the issuer must disclose, and which supervisor can act. Each regime binds only firms within its scope, once it commences.
The blockchain ecosystem is a collection of independent networks that each record transactions in a separate ledger under separate rules. They vary in how they reach agreement, whether they run programs, how often they add blocks, what they charge and how many operators would have to collude to corrupt or halt them.
A stablecoin peg holds a token near its reference price through routes to convert it at or near par. Approved customers redeem under issuer terms, any holder of an in-scope EU e-money token can by law, vault owners repay their own debt, and some contracts let any holder redeem or swap. A price off par invites a trade until the gap is below its cost.
A crypto wallet backup is a set of recovery materials that restores access to funds when the working wallet fails. It has three layers: the secret material the wallet's design requires, a written note on how the setup works, and the devices, shares or people the design depends on.
A crypto transfer is a signed instruction that moves an asset on one blockchain; once confirmed, the network generally cannot reverse it. It arrives only when three fields match what the recipient controls: the address identifies the recipient, the network identifies the ledger, and, at custodial destinations that pool customers, a memo or tag identifies the account.
Safer stablecoin use is a set of operational practices that reduce, without removing, the risks a stablecoin keeps after its design has reduced volatility against a reference asset.
机构级托管将密钥视为授权系统的一个组成部分。真正的设计对象是政策:谁可以转移什么资产、转移到何处、超过多少金额、经过多长时间延迟、需经谁批准;而技术手段(如HSM、MPC、多签名、冷存储)的存在,正是为了在不信任任何单个人或机器的情况下执行该政策。 三大技术支柱包括:硬件隔离(密钥在经过认证的HSM或安全隔离区内部生成和使用)、分布式授权(通过MPC或多签名机制确保任何单一主体均无法单独签名),以及分层流动性(冷、温、热三层存储,价值随层级递减,交易摩擦也随之降低)。 2025年2月发生的那起涉及15亿美元的Bybit盗窃案,是这个时代的决定性教训:密钥从未被提取。攻击者破坏了签名工作流,导致审批者批准了一笔恶意交易,而他们无法识别该交易的真实性质。如今,对签名内容的验证与对签名主体的保护同样重要。 监管体系更像是一块块拼凑而成的补丁,而非单一的防…
链上隐私是指区块链活动与现实世界身份可关联的程度。透明的区块链会永久公开每笔交易、金额、地址和时间戳,因此隐私完全取决于“不可关联性”:确保地址之间互不关联,且与任何姓名均无关联。链上分析攻击利用聚类启发式算法和身份锚点(如交易所记录和公开标签)来破坏这种不可关联性;而隐私实践则通过地址卫生和钱包分离来加以防御。
Oracle risk is a design risk that arises whenever an automated system acts on a price it cannot check for itself. An on-chain lending market relies on its oracle, and a centralised exchange's margin engine relies on an internal index the exchange computes.
2025年针对加密货币持有者的实体攻击达到历史新高:据CertiK分析,全球共发生72起经核实的事件,确认损失达4090万美元,实体袭击事件数量增长了250%,其中欧洲约占案件总数的40%,仅法国就记录了19起。 攻击者通过受害者自己泄露的信息来选择目标:社交媒体上的炫耀、公开的链上余额、会议出席记录,以及因数据泄露而暴露的个人信息。最经济的防御方式就是停止生成可供攻击者利用的信息。 胁迫能突破任何在威胁下可被单人绕过的安全措施。单个助记词便是最糟糕的情况:所有资产都可从一人身上、在同一地点、数分钟内被提取。分布式设计、多签名以及带有延迟和法定人数阈值的阈值方案,改变了暴力手段所能达到的效果,因为没有任何一个人能仅通过配合就获取全部余额。 控制措施只能威慑那些相信这些措施的攻击者。分层限制、时间锁以及可见的机构式流程,能在攻击开始前就降低其预期收益…
A relationship investment scam is investment fraud that begins with a relationship. A scammer, usually making contact out of the blue online, builds trust and then steers the person into depositing money, often crypto, on a counterfeit trading platform. It shows invented gains and may pay out a small early withdrawal.
私钥是一种保密的签名材料,可用于授权区块链账户或支出策略下的操作。公钥是根据私钥通过数学推导得出的,它允许网络在不获知私钥的情况下验证签名。钱包地址是根据密钥、脚本、合约或程序规则推导出的、特定于网络的标识符。大多数用户分享的是地址,而非原始公钥。助记词通常是许多确定性密钥的备份输入,而非某个私钥的同义词。
工作量证明(PoW)和权益证明(PoS)主要是更大共识系统内部的抗西比尔攻击机制和区块提议机制。比特币将区块生成与计算工作量挂钩,并通过累计工作量最多的一条链来确定有效链。 以太坊将提案和投票权重与质押的 ETH 挂钩,采用 LMD-GHOST 分叉选择机制,并通过 Casper FFG 使检查点最终确定。工作量证明会持续消耗外部资源;权益证明会使资本面临处罚和减持风险,但并非每次攻击都会摧毁攻击者全部的权益。
审计是在特定假设下对特定代码进行的、有时间限制的专家审查。它虽能降低风险,但设计上会遗漏整类故障:经济攻击、预言机信任、升级治理、编译器漏洞、链下基础设施,以及报告签署后发生的所有变化。 损失数据已发生变化。2026年上半年,智能合约漏洞利用约占事件总数的60%,但仅占损失总额的很小一部分;基础设施和密钥泄露事件约占总事件的15%,却占损失总额的76%。代码变得更难被攻破,但围绕代码的运维措施却未能跟上这一步伐。 经过审计的协议依然会出错。2025年5月,Cetus因一个被多次审计忽略的溢出检查漏洞,导致约2.23亿美元被利用,其中约1.62亿美元随后被冻结并纳入社区恢复流程;2023年,Euler因审计曾审查过的逻辑漏洞损失了1.
A stablecoin failure mode is a pattern of breakdown that stops a token being turned back into its reference value. A fiat-backed coin can break when the path to its reserves freezes through a bank failure, gated redemption or weekend closure. An algorithmic coin can break when its own defence mechanism destroys its backing.
人们因九种反复出现的失误模式而损失加密货币,其中最严重的往往与技术关系最小。欺诈行为占据主导地位:仅2025年,美国受害者报告的加密货币投资诈骗损失就达约72亿美元,是所有黑客攻击损失总额的数倍。 技术性盗窃正集中于数量更少、规模更大的事件中。2025年黑客攻击窃取了约34亿美元,其中近一半来自单一事件;到2026年上半年,这一趋势更加明显:共发生创纪录的207起事件,被盗金额不足10亿美元,其中基础设施和密钥遭入侵的案件仅占总数的六分之一,却造成了约四分之三的损失。 这两种趋势并行发展,二者之间的关系目前仅是一种假设,而非已证实的关联。 经追踪的“钱包清空”类损失从2024年的约4.
自托管仍是比特币的主要持有方式——比特币是唯一能够估算托管情况的资产:River 2025年的托管研究显示,约65%的供应量(截至撰写本文时超过8000亿美元)由持有者通过自有密钥掌控。 中介托管的份额并非在缩减,而是在发生结构性变化。在第三方托管领域,交易所的份额从2021年的过半降至约35%,而机构托管方的份额则有所增长;此外,自2024年美国批准现货ETF以来,通过ETF和财团公司等间接渠道的托管规模迅速扩张,到2025年已达到约3000亿美元,约占比特币总供应量的11.
A stablecoin comparison is a side-by-side reading of dollar tokens that records, for each one, what backs it, how that backing is evidenced, who can redeem directly with the issuer, which legal entity issues it and what has gone wrong before.
The Exchange Failure Index is a sourced register that records eight custodial crypto platform failures from 2014 to 2022 as examples, classifying each by its initial trigger and what followed, setting out the sums, how the law treated customer claims and what customers recovered, in what form and over what time.
The Stablecoin Adoption Report is a dated research assembly that quotes public measurements of stablecoin use, naming for each the instrument behind it, its reference date, its denominator and its limits.
The Wallet Vulnerability Ledger is a dated register of documented security failures in crypto wallet software, hardware and their distribution channels that records, for each incident, the affected products and versions, the disclosure date, the technical root cause, the patched status, any reported impact with its source, and a confidence label, so that implementation risk can be assessed from published evidence.
多方计算(MPC)是一个广泛的领域。阈值签名是MPC的一种应用,并非所有多方计算系统的同义词。 t-of-n 阈值签名通常需要至少 t/n 名参与者才能生成签名,其目标是在少于 t 次恶意攻击的情况下确保秘密安全。必须同时考虑可用性阈值和保密性阈值。 Shamir 秘密共享非常适合分割存储的秘密。单独使用时,它会在常规签名之前重建该秘密;而阈值签名则在份额保持分布式状态时执行签名计算。 当采用安全的分布式密钥生成协议从一开始就生成密钥份额时,完整的私钥根本无需存在。但在使用可信中间商、导入现有密钥或重建备份的系统中,完整的私钥可能存在。
双因素认证在密码之外增加了第二种独立的身份验证方式。其提供的保护程度完全取决于您选择的第二种验证方式:通过短信发送的验证码可能因手机号码被劫持而被窃取,而硬件安全密钥或通行密钥则在设计上具有抗钓鱼攻击的能力。 SIM卡交换是指将您的手机号码转移到攻击者的SIM卡上,通常是通过欺骗或贿赂运营商员工来实现的。2025年,美国联邦调查局(FBI)互联网犯罪投诉中心记录了971起SIM卡交换投诉,涉及所有犯罪类别的报告损失总额达1740万美元,该技术仍是加密货币账户劫持中的标准首步手段。 当前美国联邦指南《NIST SP 800-63B》将短信验证码归类为受限身份验证器。基于FIDO2标准的抗钓鱼方法——硬件密钥和通行密钥——是保护资金安全的推荐标准。 账户安全采用分层防护机制:来自密码管理器的唯一密码、交易所及其背后邮箱账户上具备防钓鱼功能的双因素认证、…
加密货币风险是一个分层体系,而非单一故障模式。正是那套使私钥签名在计算上难以伪造的密码学技术,也使得已签名的错误不可逆转,因此风险集中于权力集中的任何环节:合约逻辑、预言机输入、跨链桥验证者集、操作员签名工作流以及市场结构杠杆。 威胁面已向上迁移至技术栈更高层。根据Chainalysis针对特定追踪器的统计,2025年犯罪分子盗取了约34亿美元,但构成发生了变化:价值15亿美元的Bybit盗窃案是通过入侵签名接口而非合约实现的,而仅与朝鲜有关联的攻击者就盗取了约20.
每种自主托管模式对同一个问题给出了不同的答案:签名权限位于何处?软件钱包将其保存在联网设备上;硬件钱包将其隔离在专用的签名设备中,该设备专为内部存储密钥而设计;而MPC钱包则将其拆分为多个份额,确保签名过程永远无法重建完整的密钥,且当采用分布式密钥生成方案时,根本不存在完整的密钥。 关键的比较在于故障模式,而非功能特性。软件钱包的故障源于设备被入侵;硬件钱包的故障源于其仍依赖的助记词备份,以及丢失、损坏和所有者被迫交出等风险;MPC 消除了单一可复述的秘密,将风险转移到阈值被突破以及提供商或协议设计上。 丢失是“沉默的巨人”。River的2025年托管分析估计,约有157万枚比特币可能已永久丢失,并指出用户自造成的丢失不容忽视,同时强调其链上分析方法无法证实该数据,也无法确定任何币为何停止流动。存储模型的优劣取决于其恢复方案的有效性。 一个常见的解…
区块链是一种分布式账本,它将有序的交易或状态变化记录在区块中。每个区块通常引用其前一个区块,并包含对其数据的加密承诺。节点会独立验证提议的区块,并利用共识和分叉选择规则来决定接受哪条历史记录。哈希链接可揭露篡改行为;复制和最终性使得已确立的历史记录难以被替换,且替换成本高昂。
助记词是一组普通单词(通常为十二或二十四个),它编码了钱包生成密钥的主密钥。它是传统自托管模式的主备份,也是加密货币领域有史以来推出的最精妙的标准之一。 它的强大之处恰恰也是其问题所在。任何读到该短语的人,无论身处何地,都能永久地从钱包中进行消费;而任何丢失该短语且没有其他副本的人,将完全无法访问钱包。一个对象同时承载着彻底被盗和彻底丢失的风险,这正是“单点故障”的定义。 逐案记录的失败案例往往平淡无奇,而非戏剧性事件:助记词被拍照留存、被输入到虚假的技术支持页面、在家庭火灾中烧毁、在搬家时被丢弃,或是被埋入无人能开启的遗产中。 River 2025年的托管分析估计,约有157万枚比特币可能已永久丢失,并指出用户自发造成的损失相当可观;同时强调其链上分析方法无法证实这一数字,也无法确定任何币为何停止流动,因此无法对原因进行排序。 只要处理得当、存储…
比特币是一个于2009年推出的点对点电子现金和结算系统。它在公共区块链上记录所有权,并利用工作量证明机制以及独立验证节点,在无需银行介入的情况下防止双花。其原生资产比特币(BTC)按照递减的发行计划发行,总供应量上限为2100万枚。没有任何单一组织能够单方面更改用户选择执行的规则。
加密资产通常是区块链或类似分布式账本上的记录——而非存储在钱包中的文件。 私钥、智能合约规则或托管签名系统决定谁有权授权交易。 加密签名用于证明授权;网络验证和共识机制决定哪些有效交易将被纳入被接受的历史记录。 “加密货币”的概念比“数字现金”更为广泛。该类别包括货币资产、网络资产、稳定币、治理代币和实用代币、代币化债权以及其他设计形式。
多签名钱包要求在资金转移前需 m 个密钥中的 n 个进行签名:例如三分之二、五分之三。丢失一个密钥不会导致资金被冻结,被盗一个密钥也不会导致资金丢失,这正是消除单点故障的定义。 m-of-n 的选择是在两种故障方向之间进行权衡。提高阈值会增强抗盗能力,但会削弱抗丢失能力;关键在于合理配置密钥,确保没有任何单一事件、地点或个人能够转移资金或阻止资金转移。 多签名(Multisig)的法定人数要求存储在链上,透明且由网络本身强制执行;MPC(多方计算)则通过密码学在链下实现相同的法定人数属性,具有统一的签名标准、在签名方案兼容的区块链上广泛支持,以及私有策略。 机构和个人越来越多地同时采用这两种方案,而它们共有的风险在于“被欺骗的法定人数”:签名者批准了一项他们无法看清真实内容的有效载荷,这正是导致 Bybit 15 亿美元盗窃案背后的机制。 多签将托…
A dApp, or decentralised application, is an application whose core logic runs as smart contracts on a blockchain, reached through a front end such as a website, governed by whoever can change its contracts, often reliant on off-chain services and used through a wallet. The front end can only propose actions.
A network fee is the price a sender attaches to a blockchain transaction to have it included and executed, set by demand for the chain's limited block space; who receives it depends on the chain.
A crypto wallet is a key-management tool that generates addresses for receiving crypto, signs transactions to send it, and shows balances by reading the blockchain. The assets stay on the chain; the wallet holds the keys, or in some designs key shares, that authorise moving them. The word also covers custodial accounts, where a company holds the keys on the customer's behalf.
A smart contract is a program that runs on a blockchain under that chain's rules, holds assets and transfers them when a transaction calls it and its coded conditions are met. Every validator executes the same code against the same data, so no operator approves each step.
A stablecoin is a blockchain token that aims to hold a steady value, usually one US dollar, by resting on issuer-held reserves, surplus crypto locked in contracts, hedged positions or supply rules. Its holder owns the token; the right to redeem it is separate.
Blind signing is a way of approving a crypto transaction or message that commits the signer's key to data the signer cannot read or check. It happens when a wallet cannot decode the request and shows raw data, or when compromised software describes the request as something it is not. The approval then depends on trusting whoever built the request.
DeFi (decentralised finance) is a category of financial applications that runs trading, lending and derivatives as smart contracts on public blockchains. Users keep custody of their assets until a contract's rules move them. Many public markets accept any address that meets those rules, while other contracts check an allowlist, a role or an identity credential first.
Proof of reserves is a disclosure practice that lets a custodial platform prove control of on-chain addresses and, in stronger versions, commit cryptographically to its customer liabilities, so each customer can check their own inclusion and an accountant, often under agreed-upon procedures, can compare the totals. It evidences asset control and inclusion at one snapshot.
Staking is a form of participation in a proof-of-stake network that commits the network's own coin behind a validator, directly or through an intermediary, so that the stake helps propose and confirm blocks. The protocol pays participating stake a share of issuance and unburned transaction fees, in that coin, at a rate its formulas set.
A crypto reward is a token payment with an identifiable source: a protocol paying for network security, borrowers paying interest, traders paying swap fees, a project distributing promotional tokens, or a company promising a rate it sets.
“谁持有您的加密货币”实际上是在问一个问题:谁掌控着能够转移这些资产的密钥? 在托管账户中,由公司控制密钥,而您对该公司拥有资产索赔权。在经典的自托管模式下,您控制一个密钥,并由助记词作为备份。在多方密码学(MPC)自托管模式下,您通过分散在您的设备及协助者之间的密钥份额来控制资产;在设计良好的方案中,没有任何单一份额、设备或公司能够单独转移这些资产,不过特定产品能否实现这一点,取决于其签名器和恢复机制的设计。 每种模式面临的风险场景各不相同。托管账户最糟糕的情况是公司破产、冻结提现或遭遇黑客攻击,而历史上这三种情况都曾发生过。单密钥钱包最糟糕的情况是密钥丢失或被盗导致资产尽失。在设计良好的MPC方案中,最坏情况需要同时发生多个故障;这正是设计目标,而具体产品能否达到这一目标,取决于其签名机制、恢复机制及服务提供商的配置。 在便利性与控制权之间,二…
跨链桥允许价值在没有共同规则的区块链之间流动。大多数设计通过在某条链上锁定资产、在另一条链上铸造索赔来实现,这使得巨大的池化价值集中于负责验证两条链之间消息的机制之上。 该机制才是问题的关键所在。两端的链由全网共识保障安全;而中间的跨链桥通常仅依靠规模小得多的机制来保障安全:寥寥数个验证者密钥、多签机制,或是证明验证合约。 攻击者会理性地瞄准最薄弱的环节,而五起典型的跨链桥安全事件——Ronin、BNB Bridge、Wormhole、Nomad和Harmony——正是通过这一中间层遭受了超过18亿美元的攻击,在扣除资产冻结和追回金额后,实际损失远超12亿美元。 2022年,跨链桥攻击造成的损失约为20亿美元,成为当时最主要的盗窃类别。此后,损失重心已转向其他领域的运营风险和密钥泄露,部分原因是跨链桥的安全性有所提升,部分原因则是跨链桥所承载的市场…
Know-your-customer (KYC) is an anti-money-laundering control that requires regulated financial businesses to identify and verify their customers; where a jurisdiction's law covers crypto businesses, it applies to exchanges alongside record-keeping, transaction monitoring and suspicious-activity reporting. Each jurisdiction sets its own duties, thresholds and start dates.
尚无与此搜索匹配的文章。